SIM swap: $11.6 million in cryptocurrencies and 6 years in prison

  • A federal court in California on Tuesday sentenced 24-year-old Scot Tyler Buchanan to six years in prison for stealing cryptocurrencies worth at least $11.6 million.
  • The group extorted company employees’ login details via text messages, identified cryptocurrency holders and transferred their phone numbers to their SIM cards to capture login codes.
  • In June, CBZC dismantled a group in Poland operating with a similar method. Login using an application or dongle instead of SMS, as well as operator security, protects against number hijacking.

A SIM swap victim usually first sees only that the phone has lost coverage. At this time, her number is already working on the criminals’ SIM card, and the login codes from the exchange are sent to them. This is how Tyler Buchanan and his accomplices stole cryptocurrencies worth at least $11.6 million. On Tuesday, a court in Santa Ana, California, sentenced a 24-year-old Scotsman from Dundee to six years in prison, Decrypt reports.

How Buchanan’s group operated

Details from the US Department of Justice’s announcement are quoted by Security Affairs. From September 2021 to April 2023, the group sent hundreds of text messages to employees of at least a dozen companies. The links led to websites impersonating company login systems. The stolen data was sent to a Telegram channel that Buchanan ran with his partner.

Criminals used this data to find people who had cryptocurrencies. They then transferred victims’ numbers to devices they controlled and intercepted login codes sent via text message. They continued to empty their wallets. The largest single loss was suffered by a victim who lost $1.67 million in December 2022.
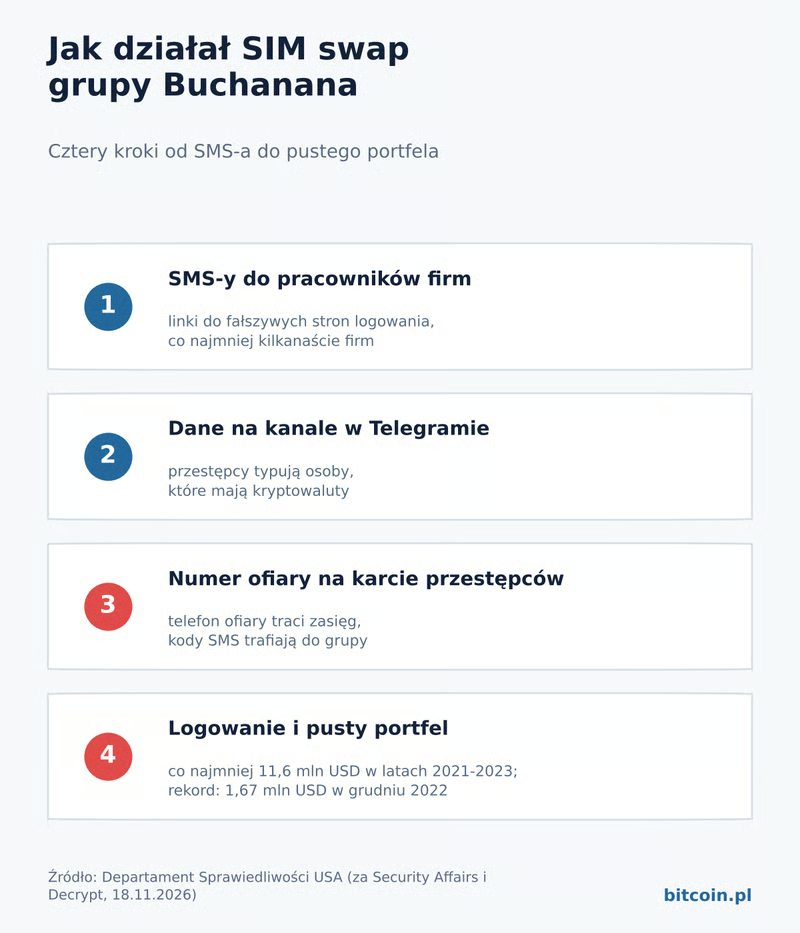
Scheme in four steps: text messages to company employees, data on the Telegram channel, the victim's number on the criminals' card, login and an empty wallet

Buchanan pleaded guilty in April to conspiracy to commit fraud and identity theft. He was detained in May 2024 at the airport in Palma de Mallorca while boarding a private plane to Naples. The Department of Justice links the case to the Scattered Spider group, known for attacks on large companies. Buchanan is the fifth and final defendant in the case. His accomplice Noah Urban previously received 10 years in prison.

Victims are still waiting for money. The court will decide at its meeting on December 11 how much the convict should pay them back.

Is SIM swap also a threat in Poland?
Yes. In June, the Central Bureau for Combating Cybercrime, with the support of the FBI, detained four members of a group that took over telephone numbers and accounts on cryptocurrency exchanges. This describes the text about how CBZC busted the SIM swap gang. According to CBZC, several dozen million zlotys passed through their hands. All four were arrested and face up to 25 years in prison.

According to BleepingComputer, the Polish group obtained victims’ data from the systems of companies cooperating with the operators and from the mailboxes of their employees. The pattern was similar to the Buchanan case: first the details from the intermediary, then the telephone number, then the stock exchange account.

Orange, Play, Plus and T-Mobile have announced a service thanks to which the bank can check whether the customer’s SIM card has recently been replaced before allowing a login or transfer. BezPrawk described it. It is not known which banks are already using it, and the announcement does not mention cryptocurrency exchanges.

What does this mean to you

If your service allows it, don’t use SMS as a second login component. The authenticator application generates the codes on your phone and does not transfer the number to the new SIM card. The dongle also protects against fake login pages, but not every exchange supports it. The step-by-step settings are described in the text on how to defend your stock exchange account after a PESEL leak.

ESET warns that fraudsters impersonate operators’ subscribers, also with forged ID cards. He advises that the operator’s codes and passwords should not be related to valid dates, and that the PESEL number should be reserved: according to the company, the operator will not issue a duplicate SIM card. If your phone suddenly loses coverage for no reason, immediately call the operator from another number. How to recognize fake SMS messages and login pages, the guide explains what phishing is.